Teradata Data Source Spectrum Reports
The reports for Administrative Privileges, System Privileges, Roles, Object Privileges, and Login Activities can be generated for Teradata data sources.
The following permissions are required for the Teradata system views and tables used by the reports:
-
select on DBC.UsersV
-
select on DBC.RolesV
-
select on DBC.RoleMembersV
-
select on DBC.AllRightsV
-
select on DBC.AccessRightsV
-
select on DBC.TablesV
-
select on DBC.LogOnOffV
-
select on DBC.DatabasesV
These permissions are necessary for the SQL queries in the fetch_report methods of the Teradata report classes. The queries access Teradata system metadata tables to retrieve information about Users, Roles, Privileges, Objects, and Login Activities. These reports are explained in detail below.
System and Security Admin Privileges Granted
The report provides information about users or roles that have been granted system-level or security administrative privileges in a Teradata database. These privileges typically allow administrative operations such as managing users, roles, or security policies. This report helps identify accounts that have elevated privileges and assists security teams in auditing administrative access across the database environment.

Object Privileges Granted with Grant Option
The report contains information about object privileges that were granted with the GRANT OPTION. When a privilege is granted with this option, the recipient can further grant the same privilege to other users or roles. This report helps identify potential privilege propagation risks by highlighting users or roles that can delegate access to database objects.

System Privileges and Roles Granted to Users
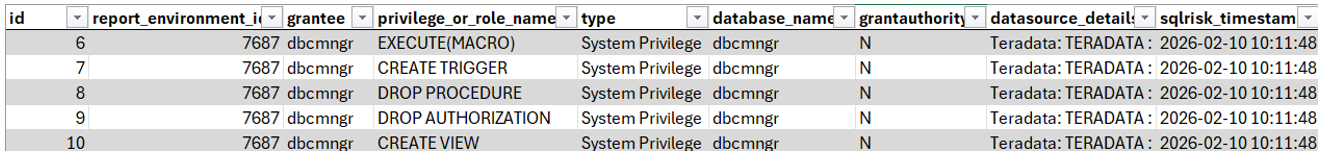
This report provides information about system privileges and roles assigned to individual users. It shows how administrative capabilities and role-based permissions are distributed across user accounts. The report is useful for auditing privilege assignments and ensuring that users only have the permissions necessary for their responsibilities.
Object Privileges by Account
The report lists object-level privileges granted to database accounts. It includes information about which users have access to specific database objects such as tables, views, or procedures. This report helps administrators understand the scope of object access across the environment and detect excessive privileges.

Execute Privileges on System Database Objects Granted to PUBLIC
The report identifies EXECUTE privileges on system database objects that have been granted to the PUBLIC role. Granting privileges to PUBLIC allows all database users to access those objects. This report is important for identifying potential security risks where sensitive system objects may be executable by all users.

Failed Logins Report
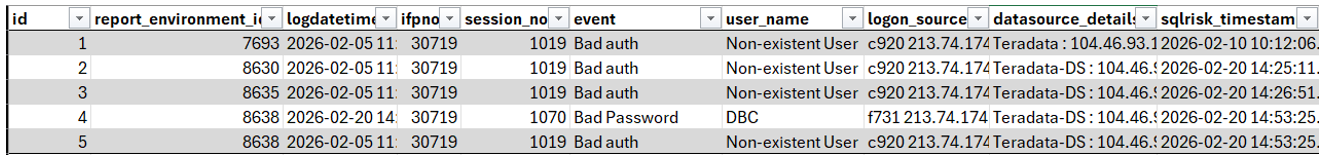
The report provides information about failed login attempts in the Teradata environment. It includes details about authentication failures, which may indicate incorrect credentials, account misconfiguration, or potential brute-force attempts. This report helps security teams monitor suspicious authentication activity and investigate possible security incidents.
Objects and System Privileges Granted to PUBLIC
This report lists database objects and system privileges that have been granted to the PUBLIC role. Since PUBLIC permissions apply to all users, this report helps identify potential overexposure of database resources. It is useful for auditing public access and ensuring that sensitive privileges are not broadly granted.

Roles Granted to Users and Roles
The report provides information about roles granted to users and other roles. It shows the role hierarchy and how privileges may propagate through role inheritance. This report is useful for understanding complex role relationships and ensuring that privilege inheritance is properly controlled.

System Privileges and Roles Granted
This report contains a consolidated view of system privileges and roles granted across the Teradata environment. It helps administrators review how privileges are distributed and detect excessive or unnecessary permissions.

User Granted Role and Table Count
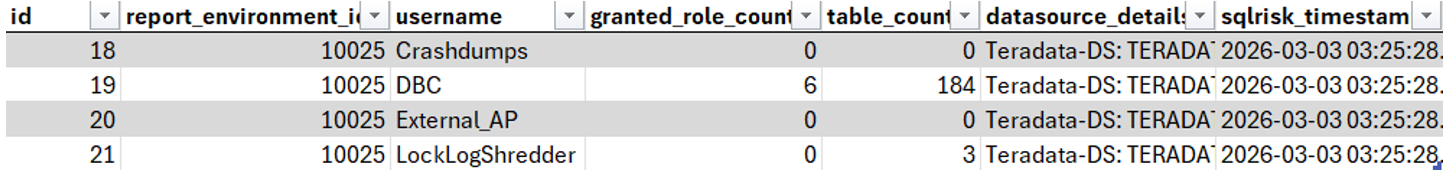
The report provides information about Teradata users, including the number of roles granted to each user and the number of tables they have access to. It helps administrators understand the scope of access each user has within the database. This report is useful for privilege auditing and identifying users with unusually broad access.
All User and Admin Count
The report provides a summary of the number of administrative and non-administrative user accounts in a Teradata database. It includes metadata about the data source and the timestamp when the report was generated. This report helps organizations assess the distribution of privileged and regular users and supports security governance efforts.
