MongoDB Data Source Spectrum Reports
The reports for All User and Admin Count, User Granted Role and Table Count, and User Privilege Report can be generated for the MongoDB data sources. The following permissions and roles are required for the following MongoDB objects:
- listDatabases on cluster
- readAnyDatabase role on the admin database
- find, listCollections, viewUser, and viewRole on all databases and collections
- find, listCollections, viewUser, and viewRole on the local database
- find, listCollections, viewUser, and viewRole on the config database
- find on the system.users collection in the admin database
- find on the system.roles collection in the admin database
These permissions are necessary for the methods in the various classes within DatabaseRepo. The code uses MongoDB commands and operations to retrieve user, role, and database information. These reports are explained in detail below.
All User and Admin Count
The report provides a summary of the number of admin and non-admin user accounts in a MongoDB database, along with details about the data source and a timestamp indicating when the data was recorded. It is useful for assessing the distribution of administrative and non-administrative users within the database.

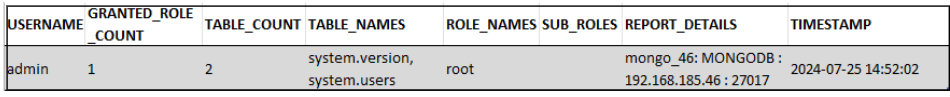
User Granted Role and Table Count
The report provides information about user accounts in a MongoDB database including the number of roles granted to each user and the data source details. It is useful for tracking user privileges and understanding the structure of user roles within the database.

User Privilege Report
The report provides details about various users and roles within a MongoDB database, including the number of roles granted, user IDs, and any associated role names. It is useful for managing and auditing user permissions and roles in the database.