Risk Overview
Databases are the main storage of actionable business information. Alongside performance, security is a major concern to continue practicing the business-as-usual activities. A key concern to visualize and often control is the privileges of the users defined in these databases. Having such information provides extensive leverage against security and compliance concerns. The number of users with administrative rights, unusual access times, multiple login attempts in a defined time range, and many more aspects of information would provide actionable data to take corrective actions if needed.
This page describes the Data Touch risk details. To view the risk dashboards, navigate to the Risk Overview menu on the left side of the Data Touch interface. Refer to Risk Overview and Risk Settings sections for detailed instructions on using the risk calculation feature.
The table below lists the risk types and categories in Data Touch DAM.
| Risk Type | Categories |
|---|---|
| DATA SOURCE RISK | EVENT_IN_RISK |
| DATA SOURCE RISK | DATA_IN_RISK |
| DATA SOURCE RISK | USER_IN_RISK |
| USER RISK | PRIVILEGE_IN_RISK |
| USER RISK | EVENT_IN_RISK |
| SYSTEM RISK | DATASOURCE_USERS_TRANSFER_FROM_REPORT |
| SYSTEM RISK | RISK_SCORE_CALCULATION |
Data Source Risk
Data Source-focused risk calculations are given in the table below.
| CATEGORY | DEFINITION | DETAIL |
|---|---|---|
| EVENT_IN_RISK | Suspicious character usage | Number of suspicious characters (defined by the administrator) used in the database |
| EVENT_IN_RISK | Nonstandard access and login times | Number of connections in the defined off-work hours |
| EVENT_IN_RISK | Exceptional volume of SQL error | Number of SQL error messages in the database |
| EVENT_IN_RISK | Suspicious client connection | Number of applications consuming the database |
| EVENT_IN_RISK | Suspicious data access on critical datasets | The number of SELECT commands sent to the columns with sensitive tagged metadata |
| EVENT_IN_RISK | Suspicious data change on critical datasets | The number of INSERT, UPDATE and DELETE commands sent to the columns with sensitive tagged metadata |
| DATA_IN_RISK | Repeated failed login | Number of failed attempts to login per database |
| DATA_IN_RISK | Sensitive data count | Number of sensitive information in the environment, tagged by metadata |
| USER_IN_RISK | System user count | Number of users with non-administrative privileges in the database |
| USER_IN_RISK | Number of users accessing critical data | Number of database users who have the privilege to send SELECT command to the columns with sensitive tagged metadata |
| USER_IN_RISK | Admin user count | Number of users with administrative privileges in the database |
User Risk
User-focused risk calculations are given in the table below.
| CATEGORY | DEFINITION | DETAIL |
|---|---|---|
| PRIVILEGE_IN_RISK | Number of system privileges | Number of system privileges (table/object) assigned per user |
| PRIVILEGE_IN_RISK | Number of granted roles | Number of roles assigned per user |
| EVENT_IN_RISK | Unexpected error on connection start | Number of connection failures to the database |
| EVENT_IN_RISK | Suspicious data access on critical datasets | The number of INSERT, UPDATE and DELETE commands sent to the columns with sensitive tagged metadata per user |
| EVENT_IN_RISK | Repeated failed login | Number of failed login attempts per user per database |
| EVENT_IN_RISK | Excessive Data Modifications | The number of INSERT, UPDATE and DELETE commands sent to the columns per user |
| EVENT_IN_RISK | Suspicious data change on critical datasets | The number of INSERT, UPDATE and DELETE commands sent to the columns with sensitive tagged metadata per user |
| EVENT_IN_RISK | Exceptional volume of SQL error | Number of SQL error messages in the database per user |
System Risk
System-focused risk calculations are given in the table below.
| CATEGORY | DEFINITION | DETAIL |
|---|---|---|
| SYSTEM | Used to retrieve user information from the Data Source using the report application | Used to retrieve user information from the Data Source using the report application |
| SYSTEM | Used to risk score calculation for user | Used to risk score calculation for user |
| SYSTEM | Used to risk score calculation for database | Used to risk score calculation for database |
Risk Analysis Overview
There are two types of risk items: Static and Dynamic.
Each risk item must be defined as one of these types.
Common Parameters
The following parameters apply to both risk types:
- Risk Score Weight
- Step Per Point (SPP)
- Running Period
- Active
Static Risk Items
- The Reference Value is provided by the user. This value represents the average normal used in calculations.
- Learning Period is not applicable and remains empty.
Dynamic Risk Items
- The system performs an observation over a defined period.
- The Learning Period is specified by the user in days.
- Observed values are averaged to calculate the average normal.
- Reference Value is not applicable and remains empty.
Risk Calculation Methodology
The Task Risk Point is calculated by measuring the percentage deviation between the new value and the normal average, normalized by the SPP value.
Formula:
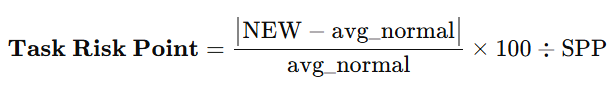
The Risk Score is calculated by applying the defined weight to the Task Risk Point.
Formula:
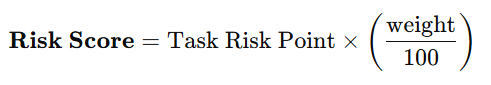
The calculated Risk Score cannot exceed the defined weight value. If the calculated score is greater than the weight, it is capped at the maximum weight.
Example Calculation
| Task | avg_normal | NEW | SPP | Task Risk Point | Weight | Risk Score |
|---|---|---|---|---|---|---|
| task1 | 100 | 140 | 1 | 40 | 10 | 4 |
| task2 | 100 | 500 | 2 | 200 | 5 | 5 |
Notes
- SPP is a double value.
- The total of all weights must be 100.
- Running period is defined using a cron expression.
- Learning period is provided in days.
- If the calculated Risk Score is negative, it is set to 0.
- The user can change the risk item type:
- Static: requires a reference value to be specified.
- Dynamic: requires a learning period to be specified.