PostgreSQL Data Source Spectrum Reports
The reports for All User and Admin Count, User Privilege Report, and User Granted Role and Table Count can be generated for the PostgreSQL data sources.
The following permissions are required for the following PostgreSQL objects:
- select on pg_roles
- select on pg_class
- select on pg_namespace
- select on pg_auth_members
- select on pg_stat_activity
- select on pg_user
These permissions are necessary for the SQL queries in the fetch_report methods of the UserPrivilegeReport, UserGrantedRoleAndTableCount, and AllUserAndAdminCount classes. The queries access system catalogs and views to retrieve user, role, and table information. These reports are explained in detail below.
All User and Admin Count
The report provides a summary of the number of admin and non-admin user accounts in a PostgreSQL database, along with details about the data source and a timestamp indicating when the data was recorded. It is useful for assessing the distribution of administrative and non-administrative users within the database.

User Privilege Report
The report contains information about user accounts in a PostgreSQL database, including their system IDs, table counts, group roles, last login times, and timestamps related to SQL risk assessments. It is useful for managing and auditing database user activity and roles.

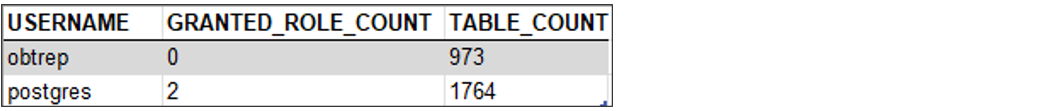
User Granted Role and Table Count
The report provides information about different PostgreSQL database users, including the number of roles granted to each user and the count of tables they have access to. It helps in understanding user privileges and the extent of their access within the database.